Showing posts with label software development company. Show all posts

Monday, 25 April 2016

Firewall Design: Strengths & Weakness

software application development companies

Introduction

Firewalls may be software based or, more commonly, purpose-built appliances. Sometimes the firewalling functions are actually provided by a collection of several different devices. The specific features of the firewall platform and the design of the network where the firewall lives are key components of securing a network. It is important for software application development companies to have a proper placement of firewall. To be effective, firewalls must be placed in the right locations on the network, and configured effectively. Best practices include:

  • All communications must pass through the firewall. The effectiveness of the firewall is greatly reduced if an alternative network routing path is available; unauthorized traffic can be sent through a different network path, bypassing the control of the firewall. Think of the firewall in terms of a lock on your front door. It can be the best lock in the world, but if the back door is unlocked, intruders don’t have to break the lock on the front door—they can go around it. The door lock is relied upon to prevent unauthorized access through the door, and a firewall is similarly relied upon to prevent access to your network. 
  • The firewall permits only traffic that is authorized. If the firewall cannot be relied upon to differentiate between authorized and unauthorized traffic, or if it is configured to permit dangerous or unneeded communications, its usefulness is also diminished. 
  • In a failure or overload situation, a firewall must always fail into a “Deny” or closed state, under the principle that it is better to interrupt communications than to leave systems unprotected. 
  • The firewall must be designed and configured to withstand attacks upon itself. Because the firewall is relied upon to stop attacks, and nothing else is deployed to protect the firewall itself against such attacks, it must be hardened and capable of withstanding attacks directly upon itself.

Firewall Strengths and Weaknesses

A firewall is just one component of an overall security architecture. Its strengths and weaknesses should be taken into consideration when designing network security at various software application development companies in India

Firewall Strengths 

Consider the following firewall strengths when designing network security:

  • Firewalls are excellent at enforcing security policies. They should be configured to restrict communications to what management has determined and agreed with the business to be acceptable. 
  • Firewalls are used to restrict access to specific services. 
  • Firewalls are transparent on the network—no software is needed on end-user workstations. 
  • Firewalls can provide auditing. Given plenty of disk space or remote logging capabilities, they can log interesting traffic that passes through them. 
  • Firewalls can alert appropriate people of specified events.


Firewall Weaknesses 

You must also consider the following firewall weaknesses when designing network security:

  • Firewalls are only as effective as the rules they are configured to enforce. An overly permissive rule set will diminish the effectiveness of the firewall. 
  • Firewalls cannot stop social engineering attacks or an authorized user intentionally using their access for malicious purposes. 
  • Firewalls cannot enforce security policies that are absent or undefined. 
  • Firewalls cannot stop attacks if the traffic does not pass through them.


Firewall Placement 

A firewall is usually located at the network perimeter, directly between the network and any external connections. However, additional firewall systems can be located inside the network perimeter to provide more specific protection to particular hosts with higher security requirements. 

Firewall Configuration 

When building a rule set on a firewall, consider the following practices:

  • Build rules from most to least specific. Most firewalls process their rule sets from top to bottom and stop processing once a match is made. Putting more specific rules on top prevents a general rule from hiding a specific rule further down the rule set. 
  • Place the most active rules near the top of the rule set. Screening packets is a processor-intensive operation, and as mentioned earlier, a firewall will stop processing the packet after matching it to a rule. Placing your popular rules first or second, instead of 30th or 31st, will save the processor from going through over 30 rules for every packet. In situations where millions of packets are being processed and rule sets can be thousands of entries in length, CPU savings could be considerable. 
  • Configure all firewalls to drop “Impossible” or “Unroutable” packets from the Internet such as those from an outside interface with source addresses matching the internal network, RFC 1918 “private” IP addresses, and broadcast packets. None of these would be expected from the Internet, so if they are seen, they represent unwanted traffic such as that produced by attackers. The software development companies must keep a check on such unwanted traffic produced by attackers.


Author Signature:  Sanika Taori

Thursday, 21 April 2016

Trends in Mobile Application Development - Part 2

software development companies

4. Implications for Developers

Hereafter we analyze the implication for developers of the three market trends presented in the previous section. In fact, the centralization of portal changes the way developers can distribute their application and reach a mass-market of consumers. The technological openness implies that developers at software development companies would use different standards to develop their application and somehow work in a more collaborative mode. Then, highly-integrated platforms offer more possibilities to develop more sophisticated applications and services. These trends can be seen as opportunities but also threats for developers. Therefore, it is crucial that developers have a good understanding of the possible implications of each trend. They need to be able to choose the platform for which they want to develop knowing all the implications.

4.1 Implications of portal centralization

Portal centralization is a major shift for developers. It allows them to reach all potential customers through one shop, which takes care of the administrative tasks, such as billing and advertising. On top of these deployment facilities comes the fact that platforms providing centralized portals count on application sales to increase their revenue and therefore heavily promote application downloads and thus widely increasing the pool of potential consumers. This promotion is mostly done through advertising, but more importantly through greatly enhanced user interfaces. Before the emergence of centralized portals it took a expert user to download and install third-party applications, usually involving an internet search and a credit card payment, on a personal computer and then a file transfer via Bluetooth. Now it has become a “one-click” operation directly executable on the mobile device. Moreover, platforms can leverage on user communities which also promote applications using the reviewing features of the shops. A negative side of strong centralization for developers is that they might have to conform to certain rules defined by the portal provider. This problem can be observed with Apple’s AppStore, which rules over which applications will be sold and which will be banned based on non-transparent criteria. To overcome these restrictions, the developer community has built alternative portals (Installer, Cydia) where developers can publish their applications. Unfortunately, only tech-savvy customers shop on such black markets, since phones must undergo a “jailbreak” procedure before they can access them.

4.2 Implications of technological openness

It is important for software development companies to know the implications of a move towards open source software offers two kinds of opportunities for application developers. First, as mentioned previously, moving towards open technology allows platform providers to reduce development costs and possibly increase the number of consumers. A greater number of platform consumers imply a greater number of potential application consumers for developers. Second, an open source project can provide career opportunities for developers willing to contribute to the platform development.

4.3 Implications of platform integration

The emergence of fully integrated end-to-end ecosystems, where the same people sell applications, manufacture devices and create their operating system, creates a coherent end-to-end approach, which makes it easier for applications to be developed, published, purchased, and used. There is less compatibility issues, which is a major problem in heterogeneous systems, where applications have to be fine-tune for specific devices with different display size for example. A drawback of high integration is the lack of alternatives if the solutions proposed by the platform do not suit the developer.

5. Conclusion 

In this paper, we described the implications that different market and technology trends have on the mobile and custom application development companies. The current evolutions show that the game for the developers has changed dramatically. There are many new opportunities for them to develop, distribute, and generate significant revenues with the emerging mobile application portals. Since the mobile application development landscape has substantially changed over the past several years, mobile development platforms have become more integrated and generally play the role of application portal, device manufacturer or both. As discussed in the paper, application portals tend to become more centralized, facilitating the link between developers and consumers. Moreover, several new platforms entered the open source community to lower their costs and possibly extend their consumer market by lowering prices and as a consequence increase their developer pool. In this changing environment, choosing for which platform to develop reveals to be challenging and we proposed three simple criteria: market size and accessibility, career opportunities, and creative freedom.


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Wednesday, 20 April 2016

Empowering People in Safety - Part 2

Software development companies

Principle 4.  Focus on Positive Consequences to Motivate Behavior. 

Control by negative consequences reduces perceptions of personal freedom and responsibility. Think about it.  Do you feel freer or empowered when you are working to avoid an unpleasant consequence or working to achieve a pleasant consequence? Unfortunately, the common metric used to rank companies on their safety performance is “total recordable injury rate” (or an analogous count of losses) which puts people in a reactive mindset of “avoiding failure” rather than “achieving success.” PBS provides proactive measures employees can achieve in order to prevent occupational injury. These days, Software development companies are focusing on People-Based Safety (PBS) as well.

We can often intervene to increase people’s perceptions that they are working to achieve success rather than working to avoid failure.  Even our verbal behavior directed toward another person, perhaps as a statement of genuine approval or appreciation for a task well done, can influence motivation in ways that increase perceptions of personal freedom and empowerment.  Of course, we can’t be sure our intervention will have the effect we intended unless we measure the impact of our intervention procedures.  Hence, the next basic premise of PBS. 

Principle 5.  Apply the Scientific Method to Improve Intervention. 

People’s actions can be objectively observed and measured before and after an intervention process is implemented.  This application of the scientific method provides critical feedback upon which to build improvement.   The acronym “DO IT” says it all:  D = Define the target action to increase or decrease; O = Observe the target action during a pre-intervention baseline period to identify natural environmental and interpersonal factors influencing it (see Principle 1), and to set improvement goals; I = Intervene to change the target action in desired directions; and T = Test the impact of the intervention procedure by continuing to observe and record the target action during and after the intervention program. 

The systematic evaluation of a number of DO IT processes can lead to a body of knowledge worthy of integration into a theory.  This is reflected in the next principle. 

Principle 6.  Use Theory to Integrate Information. 

After applying the DO IT process a number of times, you will see distinct consistencies. Certain intervention techniques will work better in some situations than others, by some individuals than others, or with some work practices than others.  You should summarize relationships between intervention impact and specific interpersonal or contextual characteristics.  The outcome will be a research-based theory of what is most cost-effective under given circumstances.  By doing this you are using theory to integrate information gained from systematic behavioral observation.   

Principle 7.  Consider the Internal Feelings and Attitudes of Others. 

Feelings and attitudes are influenced by the type of intervention procedure implemented, and such relationships require careful consideration by those who develop and deliver the intervention.  This is the essence of empathic leadership taught by PBS.   

The rationale for using more positive than negative consequences to motivate behavior (Principle 4) is based on the different feeling states resulting from using positive versus negative consequences to motivate behavior. Likewise, the way an intervention process is introduced and delivered can increase or decrease perceptions of empowerment, build or destroy interpersonal trust, and facilitate or inhibit an interdependent teamwork. 

Conclusion:

The PBS principles reviewed here provide a perspective that improves how people view injury prevention and talk about this challenge to themselves and to others.  Besides providing a paradigm that improves the quality and increases the quantity of safety conversations, PBS provides specific tools and methods, which software development companies are using extensively, for increasing safe behaviors, decreasing at-risk behaviors, and motivating participation in safety-related activities.   


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Empowering People in Safety - Part 1

Software development companies in India

Introduction

Behavior modification… safety management…. attitude adjustment… behavior based safety… culture change… cognitive alignment… person-based safety… human engineering… social influence.  All these terms used to address the human dynamics of injury prevention.  Each of these can be linked to a set of principles, procedures, or a consultant’s service which defines a particular approach to managing the human side of occupational safety. Software development companies in India are implementing these set of principles in order to manage the human side of occupational safety.  

 All of these terms, and most of the accompanying materials, are insufficient.  They are either too narrow and restricting, or too broad and nondirective.  Some focus entirely on behavior change, while others attempt to target vague and unobservable aspects of other people, like attitudes and thoughts.  Still others have the grand notion of directly targeting culture change. 
  
 All of these approaches are well-intentioned and none are entirely wrong.  The human dynamics of an organization include behaviors, attitudes, cognitions, and the context (or culture) in which these aspects of people occur.  However, some of these approaches are too equivocal or ambiguous to be practical, while others may be practical but are not sufficiently comprehensive. 

Systematic evaluations of our implementations have enabled successive refinements of procedures, as well as the discovery of guidelines for increasing effectiveness and the long-term impact of our interventions.  We also developed research based and practical support materials for the behavior-change and culture-enrichment process. 

Today we call this approach “People-Based Safety” (PBS).  It strategically integrates the best of behavior-based and person-based safety in order to enrich the culture in which people work, thereby improving job satisfaction, work quality and production, interpersonal relationships, and occupational safety and health.   

 This article is the first of a five-part series in which I explain the essential principles and procedures of PBS.  Here are the seven underlying principles of PBS.   

Seven Basics of People-Based Safety 

Principle 1: Start with Observable Behavior. 

Like behavior-based safety, PBS focuses on what people do, analyzes why they do it, and then applies a research-supported intervention strategy to improve what people do.  The improvement of others results from acting people into thinking differently rather than targeting internal awareness or attitudes so as to think people into acting differently.   However, unlike behavior-based safety, PBS considers that people can observe their own thoughts and attitudes.  Thus, people can think themselves into safer actions.  In other words, self-management requires self-dialogue or thinking as well as self-directed behavior.  

Principle 2.  Look for External and Internal Factors to Improve Behavior. 

We do what we do because of factors in both our external and internal worlds.  While behavior-based safety deals with only external factors, PBS teaches people how to address their internal thoughts, perceptions, and attitudes related to injury prevention.  A behavioral analysis of work practices can pinpoint many external factors that encourage at-risk behavior and hinder safe behavior.  But, it’s also possible for individuals to conduct a self-evaluation of their own self-talk and selective perception regarding safety related behavior, and choose to make appropriate adjustments. Safety is of utmost importance for all the software development companies and hence they attempt to identify external and internal factors to improve behavior.

Principle 3.  Direct with Activators and Motivate with Consequences. 

Activators (or signals preceding behavior) are only as powerful as the consequences supporting the behavior.  In other words, activators tell us what to do in order to receive a pleasant consequence or avoid an unpleasant consequence.  This reflects the ABC model, with “A” for activator, “B” for behavior, and “C” for consequence.  This principle is used to design interventions for improving behavior at individual, group, and organizational levels. 


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Monday, 18 April 2016

Security System Development Lifecycle

software development companies in India

The Systems Development Life Cycle 

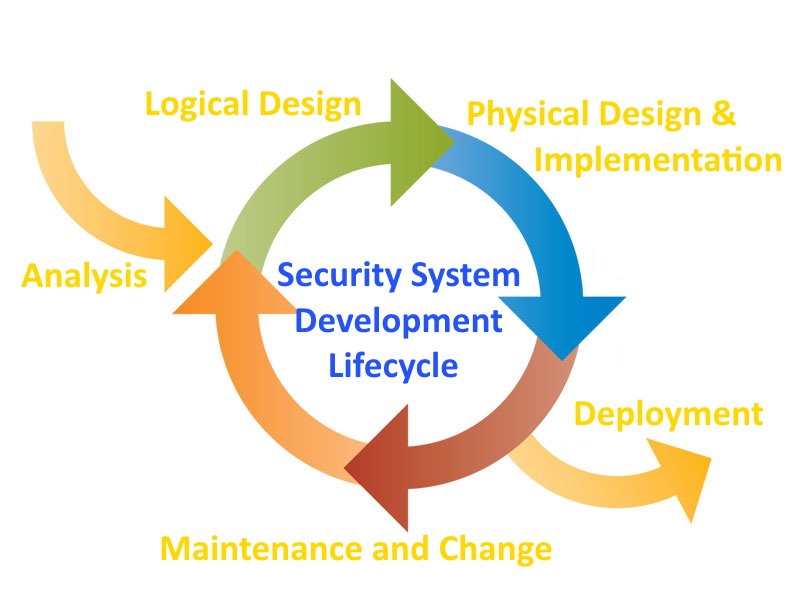
Information security must be managed in a manner similar to any other major system implemented in an organization. The one approach for implementing an information security system in an organization with little or no formal security in place is to use a variation of the systems development life cycle (SDLC): the security systems development life cycle (SecSDLC). Many software development companies in India are implementing security systems development life cycle (SecSDLC). Also to understand a security systems development life cycle, we must first understand the basics of the method upon which it is based.

Methodology and Phases 

The systems development life cycle (SDLC) is a methodology for the design and implementation of an information system. A methodology is a formal approach to solving a problem by means of a structured sequence of procedures. Also using a methodology ensures a rigorous process with a clearly defined goal and increases the probability of success. Once a methodology has been adopted, the key milestones are established and a team of individuals is selected and made accountable for accomplishing the project goals. The traditional SDLC consists of six general phases. If you have taken a system analysis and design course, you may have been exposed to a model consisting of a different number of phases. The SDLC models range from having three to twelve phases, all of which have been mapped into the six presented here. At the end of each phase comes a structured review or reality check, during which the team determines if the project should be continued, discontinued, outsourced, postponed, or returned to an earlier phase depending on whether the project is proceeding as expected and on the need for additional expertise, organizational knowledge, or other resources. Once the system is implemented, it is maintained (and modified) over the remainder of its operational life. Any information systems implementation may have multiple iterations as the cycle is repeated over time. Only by means of constant examination and renewal can any system, especially an information security program, perform up to expectations in the constantly changing environment in which it is placed. The following sections describe each phase of the traditional SDLC.20

The first phase, investigation, is the most important. What problem is the system being developed to solve? The investigation phase begins with an examination of the event or plan that initiates the process. During the investigation phase, the objectives, constraints, and scope of the project are specified. A preliminary cost-benefit analysis evaluates the perceived benefits and the appropriate levels of cost for those benefits. At the conclusion of this phase, and at every phase following, a feasibility analysis assesses the economic, technical, and behavioral feasibility of the process and ensures that implementation is worth the organization’s time and effort.

Analysis 

The analysis phase begins with the information gained during the investigation phase. This phase consists primarily of assessments of the organization, its current systems, and its capability to support the proposed systems. Analysts begin by determining what the new system is expected to do and how it will interact with existing systems. This phase ends with the documentation of the findings and an update of the feasibility analysis.

Logical Design 

In the logical design phase, the information gained from the analysis phase is used to begin creating a systems solution for a business problem. In any systems solution implemented at any software development company, it is imperative that the first and driving factor is the business need. Based on the business need, applications are selected to provide needed services, and then data support and structures capable of providing the needed inputs are chosen. Finally, based on all of the above, specific technologies to implement the physical solution are delineated. The logical design is, therefore, the blueprint for the desired solution. The logical design is implementation independent, meaning that it contains no reference to specific technologies, vendors, or products. It addresses, instead, how the proposed system will solve the problem at hand. In this stage, analysts generate a number of alternative solutions, each with corresponding strengths and weaknesses, and costs and benefits, allowing for a general comparison of available options. At the end of this phase, another feasibility analysis is performed.

Physical Design 

During the physical design phase, specific technologies are selected to support the alternatives identified and evaluated in the logical design. The selected components are evaluated based on a make-or-buy decision (develop the components in-house or purchase them from a vendor). Final designs integrate various components and technologies. After yet another feasibility analysis, the entire solution is presented to the organizational management for approval.

Implementation 

In the implementation phase, any needed software is created. Components are ordered, received, and tested. Afterward, users are trained and supporting documentation created. Once all components are tested individually, they are installed and tested as a system. Again a feasibility analysis is prepared, and the sponsors are then presented with the system for a performance review and acceptance test.

Maintenance and Change 

The maintenance and change phase is the longest and most expensive phase of the process. This phase consists of the tasks necessary to support and modify the system for the remainder of its useful life cycle. Even though formal development may conclude during this phase, the life cycle of the project continues until it is determined that the process should begin again from the investigation phase. At periodic points, the system is tested for compliance, and the feasibility of continuance versus discontinuance is evaluated. Upgrades, updates, and patches are managed. As the needs of the organization change, the systems that support the organization must also change. It is imperative that those who manage the systems, as well as those who support them, continually monitor the effectiveness of the systems in relation to the organization’s environment. When a current system can no longer support the evolving mission of the organization, the project is terminated and a new project is implemented.

Securing the SDLC 

Each of the phases of the SDLC should include consideration of the security of the system being assembled as well as the information it uses. Whether the system is custom and built from scratch, is purchased and then customized, or is commercial off-the-shelf software (COTS), the implementing organization such as software development company is responsible for ensuring it is used securely. This means that each implementation of a system is secure and does not risk compromising the confidentiality, integrity, and availability of the organization’s information assets. The following section, adapted from NIST Special Publication 800-64, rev. 1, provides an overview of the security considerations for each phase of the SDLC.


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Thursday, 14 April 2016

Implementing ISO 27001 - Part 2

Software development companies

Implementation Phases

An organization needs to have the detailed understanding of PDCA implementation phases to manage the costs of the project. Software development companies adopt PDCA cycle to implement international standards. Cycle of the PDCA is consistent with all auditable international standards: ISO 18001, 9001 and 14001. ISO/IEC 27001:2005 gives the following PDCA steps for an organization to follow:
  • Define an ISMS policy.
  • Define the scope of the ISMS.
  • Perform a security risk assessment.
  • Manage the identified risk.
  • Select the controls to be implemented and applied.
  • Prepare an SOA.


Phase 5—Prepare an Inventory of Information Assets to Protect, and the Rank Assets According to the Risk Classification Based on Risk Assessment

The various companies, such as software development companies, needs to create a list of information assets to be protected. The following are suggested steps:
  • For the assets classify the key CIA impact levels: high, medium and low.
  • Identify the risks, and also classify them according to their severity and vulnerability.
  • After complete identification of the risks and the levels of CIA, do assign the values to the risks.


Phase 6—Manage the Risks, and Create a Risk Treatment Plan

To control the impact associated with risk, the organization must accept and avoid and transfer or reduce the risk to an acceptable level using risk mitigating controls. Then the next stage is performing the gap analysis with the controls provided in the standard to create an RTP and an SOA and it is also important to obtain management approval of the proposed residual risks.
The RTP also provides:
  • Acceptable risk treatment (accept, transfer, reduce, avoid)
  • Identification of operational controls and additional proposed controls with the help of gap analysis


Phase 7—Set Up the Policies and Procedures to Control Risks

For the controls adopted, shown in the SOA the organization will require the statements of policy or a detailed procedure and responsibility document to identify user roles for consistent and effective implementation of policies and procedures. And the documentation of policies and procedures is a requirement of ISO/IEC 27001. Also the list of applicable policies and procedures depends on the organization’s structure, the locations and the assets.

Phase 8—Allocate Resources, and Train the Staff

The ISMS process highlights one of the important commitments for the management: sufficient resources to manage, develop, maintain and implement the ISMS. And also it is very essential to document the training for audit.

Phase 9—Monitoring the Implementation of the ISMS

The periodic internal audit is a must for monitoring and review. The internal audit review consists of testing of controls and identifying corrective/preventive actions. In order to complete the PDCA cycle all the gaps identified in the internal audit must be addressed by identifying the corrective and preventive controls needed and the company’s compliance based on a gap analysis.

Also to be effective, the ISMS need to be reviewed by management at periodic and planned intervals. This review follows the changes and improvements to the policies, procedures, the controls and staffing decisions. It is a very important step in the process is project management review. Thus the results of audits and periodic reviews are documented and maintained.

Phase 10—Preparation for the Certification Audit

In order for the organizations, such as software development companies, to be certified it is very essential that it conduct a full cycle of internal audits and management reviews and activities in the PDCA process and that it retains evidence of the responses taken as a result of those reviews and audits. The ISMS management should review risk assessments, the RTP, the SOA, and the policies and procedures at least annually.

An external auditor will first examine the ISMS documents to determine the scope and content of the ISMS and the objective of the review and audit is to have sufficient evidence and review/audit documents sent to an auditor for review. Thus the evidence and documents will demonstrate the efficiency and effectiveness of the implemented ISMS in the organization and its business units.

Phase 11—Conducting Periodic Reassessment Audits

The follow-up reviews or periodic audits confirm that the organization remains in compliance with the standard.

The certification maintenance requires periodic reassessment audits to confirm that the ISMS continue to operate as specified and intended. Thus with any other ISO standard the ISO 27001 follows the PDCA cycle and assists ISMS management in knowing how far and how well the enterprise has progressed along this cycle. It directly influences the time and cost estimates related to achieving compliance.

Conclusion

The true success of ISO 27001 is its alignment with the business objectives and effectiveness in realizing those objectives. For software development companies the IT and other departments play an important role in implementing ISO 27001. Implementing ISO 27001 is an exercise toward better understanding an existing inventory of IT initiatives, information availability and ISMS implementation phases. An organization also needs to have the detailed understanding of PDCA implementation phases. 

Without a well-defined and well-developed ISO 27001 project plan, implementing ISO 27001 would be a time- and cost-consuming exercise. To achieve the planned return on investment (ROI), the implementation plan has to be developed with an end goal in mind. Training and internal audit are major parts of ISO 27001 implementation. ISO 27001 certification should help assure most business partners of an organization’s status with respect to information security without the necessity of conducting their own security reviews. 


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Implementing ISO 27001 - Part 1

Software development companies

Implementation Phases

An organization needs to have the detailed understanding of PDCA implementation phases to manage the costs of the project. Software development companies adopt PDCA cycle to implement international standards. Cycle of the PDCA is consistent with all auditable international standards: ISO 18001, 9001 and 14001. ISO/IEC 27001:2005 gives the following PDCA steps for an organization to follow:


  • Define an ISMS policy
  • Define the scope of the ISMS
  • Perform a security risk assessment
  • Manage the identified risk
  • Select the controls to be implemented and applied
  • Prepare an SOA


Phase 1—Identify Business Objectives

Stakeholders must buy in; identifying and prioritizing objectives is the step that will gain management support. The primary objectives can be derived from the company’s mission, the strategic plan and IT goals. The objectives are:


  • Increased marketing potential
  • Complete assurance to the business partners of the organization’s status with respect to information security
  • Both Increased revenue and profitability by providing the highest level of security for customers’ sensitive data
  • Identification of the information assets & effective risk assessments
  • Compliance with industry regulations


Phase 2—Obtain Management Support

Management must make a commitment to the establishment, planning, the implementation, the operation, monitoring, review, improvement and maintenance of the ISMS. The commitment must also include activities such as ensuring that the proper resources are available to work on the ISMS and that all employees affected by the ISMS have the proper training, competency and also awareness. The following activities/initiatives show management support:


  • An information security policy
  • The information security objectives & the plans
  • The roles & responsibilities for the information security or a segregation of duties (SoD) matrix that shows the list of the roles related to information security
  • Sufficient resources for managing, developing, maintaining and implementing the ISMS
  • The determination of acceptable level of risk
  • The management reviews of the ISMS at planned intervals
  • Assurance that personnel affected is also affected by the ISMS are provided with training
  • Appointment of the competent people for the roles and responsibilities that they are assigned to fulfill


Phase 3—Select Proper Scope of Implementation

ISO 27001 states that any scope of implementation may cover all or part of an organization. According to it for the software company or any other company the scope of the ISMS, the processes, business units, external vendors or contractors falling within the scope of implementation must be specified for certification to occur.

The standard also thus requires companies to list any scope exclusions and the reasons why they were excluded.

Identifying the scope of implementation can save the organization time, money. The following points should be considered:


  • Selected scope helps to achieve all the identified business objectives.
  • The organization’s over all scale of operations is an integral parameter needed to determine the compliance process’s complexity level.
  • To find out appropriate scale of operations, organizations need to consider the number of employees, business processes, work locations, and products or services offered.


Phase 4—Define the appropriate Method of Risk Assessment

To meet the requirements of ISO/IEC 27001, the companies need to define & document the method of risk assessment. The ISO/IEC 27001 standards do not specify the risk assessment method that can be used. The following all points should be considered:


  • The method that can be used that can assess the risk to identified information assets
  • Which risks are intolerable therefore, that need to be mitigated
  • Managing the residual risks through carefully considered policies, the procedures and controls
  • Choosing a risk assessment method is one of the most important parts of establishing the ISMS and use of the following will be helpful:
  • NIST Special Publication (SP) 800-30 Risk Management Guide for Information Technology Systems
  • Sarbanes-Oxley IT risk assessment
  • Asset classification, data classification documents (determined by the organization)
  • ISO 27001 needs risk evaluations based on levels of confidentiality, integrity and availability (CIA):
    • Confidentiality—Clause 3.3: Ensuring that information is accessible only to those authorized to have access
    • Integrity—Clause 3.8: Safeguarding the accuracy and completeness of information and processing methods
    • Availability—Clause 3.9: Ensuring that authorized users have access to information and associated assets when required


Conclusion

The true success of ISO 27001 is its alignment with the business objectives and effectiveness in realizing those objectives. For any software development company, IT & the other departments play an important role in implementing the ISO 27001. Implementation of ISO 27001 is an exercise toward better understanding an existing inventory of IT initiatives & the information availability and ISMS implementation phases. The organization also needs to have the detailed understanding of PDCA implementation phases. 

Without a well-defined and well-developed ISO 27001 project plan & implementing ISO 27001 would be a time- and cost-consuming exercise & to achieve the planned return on investment (ROI), the implementation plan has to be developed with an end goal in mind. Training and internal audit are major parts of ISO 27001 implementation. ISO 27001 certification should help assure most business partners of an organization’s status with respect to information security without the necessity of conducting their own security reviews. 


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Wednesday, 13 April 2016

Planning for ISO 27001 - Part 1

web application development companies

Introduction

ISO/IEC 27001:2005 Information Technology— Security techniques—Information security management systems—Requirements is an information security management system (ISMS) standard published in October 2005 by the InternationalOrganization for Standardization (ISO) and International Electro technical Commission (IEC).The potential benefits of implementing ISO 27001 and obtaining certification are numerous also implementing ISO 27001 enables enterprises to benchmark against competitors and to provide relevant information about IT security to vendors and customers, it enables management to demonstrate due diligence. And it also can foster efficient security cost management, and compliance with laws & regulations, a comfortable level of interoperability due to a common set of guidelines followed by the partner organization. It also helps in improving IT information security system quality assurance (QA) and increase security awareness among the employees, customers and the vendors, etc., and it can also increase IT and business alignment. And it also provides a process framework for IT security implementation and can also assist in determining the status of information security and the degree of compliance with the security policies, the directives and standards. Many software development companies, custom application development companies, web application development companies etc are leveraging benefits of implementing ISO 27001.

Costs of Implementation

Before implementing ISO 27001, one needs to consider the costs and project length all of which are further influenced by the detailed understanding of the implementation phases. Also in today’s cloud computing environment, the organizations that want to reduce costs without compromising information security are looking at ISO 27001 certification as a promising means to provide knowledge about their IT security. Implementation costs are driven by the perception of risk and how much risk an organization is prepared to accept. Companies such as software development companies incur various costs while implementation. In total four costs need to be considered when implementing this type of project:

1. Internal resources—The system covers a wide range of business functions which include management, human resources (HR), IT, facilities and security. All these resources will be required during the implementation of the ISMS.

2. External resources—Experienced consultants will save a huge amount of time and cost. Also they will prove useful during internal audits and ensure a smooth transition toward certification.

3. Certification—Only a few approved certification agencies currently assess companies against ISO 27001, although fees are not much more than against other standards.

4. Implementation—These costs depend largely on the health of IT within the organization. Thus if, as a result of a risk assessment or audit, a gap appears, then the implementation costs are bound to go up based on the solution implemented.


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Tuesday, 12 April 2016

Legal Infrastructure on Industrial Safety - Part 3

EMERGING ISSUES

General Legislation on Occupational Safety and Health

At present, separate statutes are enacted covering safety and health aspects of workers employed in some sectors such as factories, mines, ports and docks and construction. Many branches of economic activities are out of coverage of OSH Legislation. There is a need for enactment of a general legislation to secure safety and health of persons at work as well as other persons, against the risks arising out of or in connection with the activities at all places of work(software development firm in ahmedabad).

National Board for Accreditation in Occupational Safety and Health

The existing statutes on safety and health require regulation, recognition, certification, approvals etc. in respect of many of the requirements. Since there are multiple agencies namely, CIFs of various States/UTs, it is felt that there should be a single agency.

Self-Certification and Third Party Certification

In order to reduce the burden of inspection, a system of self-certification regarding compliance with OSH standards can be introduced. The factories employing less than 50 workers could be required to furnish the Annual Return on the compliance with the certain provisions of the Factories Act, 1948. These Returns can be accepted as a self-certification and no inspection may be undertaken in respect of such factories. However, inspections can be carried out in case of complaints, accidents, etc. Any non-compliance detected during such inspection should be taken very seriously and the occupier and manager of such factories can be severely punished. A system of self-certification in respect of compliance with labour laws has been introduced by certain States such as Gujarat, Punjab, Uttar Pradesh, etc.

Protection of Women Workers vis-à-vis Equal Opportunities

In the era of globalization and liberalization, equal opportunities to male and female workers have become essential feature of any business enterprise. At international level also women employees are contributing significantly in the growth of business. Therefore, the restrictive provisions under the statutes seem to be discriminating and many women organizations(Empowring Woman worker in Software development company in india) have taken up the issue at social, political and judicial levels.

Conclusion

In India, a national system on Occupational Safety and Health in the form of policy, statutes and regulatory mechanism exists in respect of certain branches of economic activities namely, factories, mines, ports and docks and construction. However, there is a need to extend the OSH coverage to all other sectors, through appropriate means. Further, with the phenomenal growth in the industrial sector, a system of self-certification and third party certification in the field of OSH is essential in order to reduce the burden of inspection.


References

1. Constitution of India
2. The Factories Act, 1948
3. The Model Rules under the Factories Act, 1948;
DGFASLI 1998
4. Annual Report 2007-2008; Ministry of Labour &
Employment
5. DGFASLI Standard Reference Note 2006; DGFASLI
April 2007


Legal Infrastructure on Industrial Safety - Part 2

LEGAL FRAMEWORK

As per the allocation of business rules under the Constitution, labour is in the concurrent list of subjects. It is dealt with by the MOLE at the Central and Departments of Labour under State Governments in respective States / UTs. The MOLE has enacted workplace safety and health statutes concerning workers in the manufacturing sector, mines, ports and docks and in construction sectors. Many software development companies have also adopted the legal framework. Further, other Ministries of the Government of India have also enacted certain statutes relating to safety aspects of substances, equipment, operations etc. Some of the statutes applicable in the manufacturing sector are discussed below :-

The Static and Mobile Pressure Vessels (Unfired) Rules, 1981

These (SMPV) Rules are notified under the Explosives Act, 1884. These rules regulate storage, handling and transport of compressed gases. These rules stipulate requirements regarding construction and fitments, periodic testing, location, fire protection, loading and unloading facilities, transfer operations etc. in respect of pressure vessels whose water capacity exceeds one thousand liters.

The Manufacture, Storage and Import of Hazardous Chemicals Rules (MSIHC), 1989

These MSIHC Rules are notified under the Environment (Protection) Act, 1986. These rules are aimed at regulating and handling of certain specified hazardous chemicals. The rules stipulate requirements regarding notification of site, identification of major hazards, taking necessary steps to control major accident, notification of major accident, preparation of safety report and on-site emergency plan; prevention and control of major accident, dissemination of information etc by the custom software development company in india. These rules are notified by the Ministry of Environment and Forests (MOEF) but enforced by the Inspectorates of Factories of respective States / UTs in the manufacturing sector.

REGULATION OF SAFETY AND HEALTH IN FACTORIES

The Factories Act, 1948 is applicable to the premises where(i) manufacturing process is carried on with the aid of power employing 10 or more persons; (ii) manufacturing process is carried on without the aid of power employing 20 or more persons;(iii) notified under Section 85 of the Factories Act, 1948. The State Governments are empowered to make rules under the enabling provisions as well as general provision. The State Governments are also empowered to appoint inspectors and the Chief Inspector. Thus, the State Inspectorates of Factories enforce the provisions under the Act and Rules. The uniformity in States Rules notified by different States / UTs is sought through framing of Model.


References

1. Constitution of India
2. The Factories Act, 1948
3. The Model Rules under the Factories Act, 1948;
DGFASLI 1998
4. Annual Report 2007-2008; Ministry of Labour &
Employment
5. DGFASLI Standard Reference Note 2006; DGFASLI
April 2007


Legal Infrastructure on Industrial Safety - Part 1

INTRODUCTION

At the global level, industrial safety has been drawing attention of international agencies such as ILO, WHO, UNDP, UNEP, etc. In fact, efforts are being made to consider and recognize occupational safety and health as one of the human rights.


POLICY FRAMEWORK

Constitutional Provisions

The Constitution of India under the Directive Principles of State Policy provides for certain safeguards to workers. The State policies should be directed to ensure that health and strengths of workers are not abused and just and humane conditions of work and maternity relief that are provided. The Constitution prohibits employment of child below 14 years of age for work in any factory, or mine or any hazardous occupation. The constitution also provides for the State to make any special provision for women and children.

ILO Conventions

The International Labour Organization (ILO) is the standard making body in the area of labor and social issues. The ILO was established in the year 1919. Since then, they have formulated 188 Conventions relating to conditions of labor. In addition, they have also formulated several recommendations, codes of practices and guidelines for the benefit of member countries. As one of the founder members, India has so far ratified 41 Conventions.

As a step towards facilitating the ratification, a national policy on occupational safety, health and environment at workplace is already prepared by the Ministry of Labour and Employment (MOLE). The policy is under advanced stage of declaration.

National Policy On Occupational Safety, Health And Environment At Work

The national policy aims at improvement in the safety, health and environment at workplace (especially at Manufacturing sites, Chemical industries, software development companies) through:- (i) statutory framework on OSH in respect of all sectors of economic activities (ii) facilitation of technical support services (iii) providing incentives to employees and employers (iv) establishment and maintaining of R & D capabilities in the area of risk management (v) focusing on prevention strategies; and (vi) competence enhancement of technical manpower.

The policy sets its objective to achieve continuous reduction in work related injuries, diseases and associated costs; and continuous enhancement of awareness regarding safety, health and environment. The policy also outlines an Action Programme for achieving these objectives and goals. It identifies 9 key strategies :-
1. Enforcement
2. Development of national standards
3. Compliance
4. Awareness
5. Research and development
6. Skills development
7. Data collection
8. Practical guidance
9. Incentives

National Policies On Other Subjects

The Government of India have also formulated National Environment Policy, National Policy on Petroleum, Chemicals and Petro-chemical Investment Regions (PCPIR), Policy on Information Technology Investment Regions, National Fertilizer Policy, etc. These policies also contain reference to the occupational safety and health aspects of working population. Apart from these, at the instance of National Human Rights Commission (NHRC), a national programme on ‘Elimination of Silicosis’ is being formulated.

Further, a separate legislation concerning safety, health, social security and welfare of workers employed in unorganized sectors is also being contemplated by software development company in india.


Tripartite Consultations

The MOLE has put in place a tripartite consultative mechanism in the form of Indian Labour Conference (ILC), to discuss the issues relating to labour including occupational safety and health. The ILC is assisted by another tripartite forum, Standing Labour Committee (SLC) which frames the agenda for the ILC. Further, MOLE has also constituted Tripartite Committee on ILO Conventions which addresses the issue of ratification of ILO Conventions. In addition, Tripartite Committees are also constituted as per the enabling provisions under various statutes concerning safety and health.


References

1. Constitution of India
2. The Factories Act, 1948
3. The Model Rules under the Factories Act, 1948;
DGFASLI 1998
4. Annual Report 2007-2008; Ministry of Labour &
Employment
5. DGFASLI Standard Reference Note 2006; DGFASLI
April 2007
6. www.ilo.org
7. www.labour.nic.in
8. www.dgfasli.nic.in

Sunday, 10 April 2016

Types of Software Quality Models

software development companies

1. McCall Model 

McCall’s model was developed by the Rome air development center (RADC), the US air-force electronic system decision (ESD), general electric, in order to improve the quality of software products at software development companies. The model was developed to assess the relationships between external factors and product quality criteria. The quality characteristics were classified in three major types, eleven such factors which describe the external view of the software (user view), 23 quality criteria which describe the internal view of the software (developer view), and the metrics which define and are used to provide a scale and method for measurement. The total number of factors was reduced to eleven in order to simplify it. Those factors are Correctness, Integrity, Reliability, Efficiency, Usability, Flexibility, Maintainability, Reusability, Testability, Portability, and Interoperability. The major contribution of this model is the relationship between the quality characteristics and metrics. But, this model does not consider directly on the functionality of software products.

2. Boehm Model

Boehm added new factors to McCall’s model with emphasis on the maintainability of software product at software development companies. The main aim of this model is to address the contemporary shortcomings of models that automatically and quantitatively evaluate the quality of software. Thus, Boehm model represents the characteristics of the software product hierarchically in order to get contribute in the total quality. Also, the software product evaluation considered with respect to the utility of the program. But, this model contains only a diagram without any suggestion about measuring the quality characteristics.

3. FURPS Model

FURPS model was proposed by and Hewlett-Packard Co and Robert Grady. The attributes were classified into two main categories according to the user’s requirements, the functional and non-functional requirements. Functional requirements (F): Defined by input and expected output. Non-functional requirements (URPS):

Usability, reliability, performance, supportability. Also, this model was extended by IBM Rational Software – into FURPS+. Thus, this model considered only the user’s requirements and disregards the developer consideration. But, this model fails to take into account the software some of the product characteristics, like maintainability and portability.

4. Dromey Model

Dromey (1995) states that the evaluation is different for each product, thus a dynamic idea for process modeling is required. Thus, the main idea of the proposed model was to obtain a model broad enough to work for different systems. Also the model seeks to increase understanding of the relationship between the attributes (characteristics) and the sub-attributes (sub-characteristics) of quality. Also this model defined two layers, the high-level attributes and subordinate attributes. Therefore, this model suffers from lack of criteria for measurement of software quality.

5. ISO IEC 9126 Model

As, many software quality models were proposed, the confusion happened and new standard model was required. Thus, ISO/IEC JTC1 began to develop the required consensus and encourage standardization world-wide. The ISO 9126 is part of the ISO 9000 standard, and it is the most important standard for quality assurance. The first considerations originated in 1978, and in the year 1985 the development of ISO/IEC 9126 was started.

In this model, for software development companiesthe totality of software product quality attributes was classified in a hierarchical tree structure of characteristics and sub characteristics. And the highest level of this structure consists of the quality characteristics and the lowest level consists of the software quality criteria. This model specified six characteristics including Functionality, the Reliability, Usability, Efficiency, Maintainability and the Portability; all of which are further divided into 21 sub characteristics. All these sub characteristics are manifested externally when the software is used as part of a computer system, and thus are the result of internal software attributes. All the defined characteristics are applicable to every kind of software, including computer programs and data contained in firmware and provide consistent terminology for software product quality. And they also provide a framework for making trade-offs between software product capabilities.


Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)

Tuesday, 5 April 2016

Origin & Growth of Software Development Industry

custom application development company India

1. Introduction

The custom application development company India industry was started by Mumbai-based conglomerates which entered the business by supplying global IT companies located overseas with programmers. Their success owed to the innovative exploitation of a new global market opportunity and protection from transnational corporations (TNCs) and startups by policy. In India, government policy disfavoured all types but was not at all hostile to domestic and large firms. The environment was protected and it restricted the growth of project management and domain skills so that, despite access to a large pool of programmers, the industry was not able to grow in value-addition. A decade later, mainframe-based programming and manufacturer-specific operating systems and languages gave way to workstation-based programming and standard operating systems and high-level languages. These changes modularized the programming function, now programming could be done independently of the hardware platform and from the other functions of software creation, such as system design. This, along with policy reforms that reduced costs of imported hardware and software, caused the Indian industry to shift from supplying programmers to supplying software programs.

2. Origins of the IT industry

IBM created the independent software vendor (ISV) industry in 1969 to unbundle its mainframe operating system, hardware and applications software by creating open standards.
Software is usually classified by customization and by type of use.
Types of software by usage:
1. System-level software: programs that manage the internal operations of the computer, such as driver software, operating system software and virus scan software and utilities.
2. Tools software: Programs that help applications to work better, for example database management software.

3. Applications: Programs that deliver solutions to the end-user, such as financial accounting software and word processing software.
In the 1980s, the PC was invented. The Wintel standard became established by the mid-1980s, leading to a decline in hardware prices and rising demand for the applications. The PC was for retail users, who were reliant on product software. Those PCs lacked both the programming capacity and performance needed by enterprises. Therefore, it had no impact on the custom software business.

3. The growth of India’s IT industry

The implantation of a technically sophisticated industry like software into a less developed host country has typically been explained by the access of transnational corporations to local resources facilitated by policy reforms. Tier-2 cities like Bangalore, Pune, Ahmedabad, etc. began to grow in importance in consequence. It had several advantages: (1) Infrastructure was cheaper: Firms were attracted by cheaper real estate as compared to metros software technology parks was established in such cities. (2) Labor was cheaper. (3) Many MNCs came to India; these included the pioneers IBM, HP, Accenture, Oracle, GE and Dell. In today’s date many custom software development services India have come up in the Indian market which offers very unique and useful services.

4. Conclusion

The article explained the evolution of software development services India Industry from its origins in 1974 to the present time. Domestic entrepreneurship drove the industry’s origination, survival and innovation. The private sector, found an innovative solution, that of exporting programmers instead. The growth of the industry, which happened in the mid-1980s, was preceded by a paradigmatic shift in government policy from hostility to the private sector to support for it. This article’s contribution to the literature is to show that it is possible to develop sophisticated industries even when many of the conditions that have typically been required elsewhere are missing. But, the absence of certain initial conditions, notably the absence of supportive policies to induce TNCs, can cause certain weaknesses to be embedded in the industry. 

Author Signature: Shreyans Agrawal (ifour.shreyans.agrawal@gmail.com)